Browser refresh attack
Browser refresh attack is attack which enables an adversary to obtain application credentials by going by to previous page and re-submitting the expired-document.
How to perform:
- Log into to https://<some-site>/login
- Once logged in, try for change password and logout.
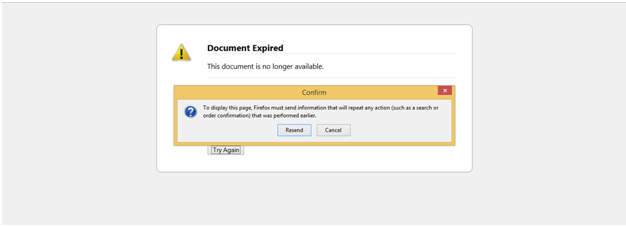
- Press "Back" on the browser window. Now you'll see the "Document Expired" page.
- Now run an interceptor (burp/tamper data)
- Click "Try again" on the web page
- Click "Re-send data"
- Watch the intercepted request.

You'll observe that login passwords being resubmitted by browser get captured.
Comments
Post a Comment