Posts

Browser refresh attack

Image
Browser refresh attack is attack which enables an adversary to obtain application credentials by going by to previous page and re-submitting the expired-document. How to perform: Log into to https://<some-site>/login Once logged in, try for change password and logout. Press "Back" on the browser window. Now you'll see the "Document Expired" page. Now run an interceptor (burp/tamper data) Click "Try again" on the web page Click "Re-send data" Watch the intercepted request. You'll observe that login passwords being resubmitted by browser get captured.

Snapdeal.com - Cross Site Scripting #Bug (DOM Based)

Image
It was shocking to get a XSS vulnerability in Snapdeal.com. Recently, I was using snapdeal for purchasing for some goods but when i tried my luck for XSS, it was hardly a matter of seconds. Basically it was DOM based XSS. The requested payload was not going to server. Instead it was being include in DOM itself and executes on browser. Proof of Concept: I used this URL with bcrumbSearch parameter which was used for searching the product name from DOM. As you try to use this URL, script get executes on browser and I got a million dollar smile. Aftermath : As a responsible security researcher, I reported this issue to help@snapdeal.com and support@snapdeal.com. I didn't got any reply from their side yet but meanwhile issue got patched without any intimation.

JQuery UI 1.11.4 Cross Site Scripting

Vulnerability name: XSS Reflected JQuery UI 1.11.4  I think nearly everyone gets shocked, when your Acunetix shows Cross Site Scripting in Jquery UI. But, may be many of you don’t know how to exploit it. So, here is a Code which will explain how to exploit vulnerabilities like these. Place the script on dialog function as shown in the Code below. <!DOCTYPE html> <html xmlns="http://www.w3.org/1999/xhtml"> <head>     <title>XSS in closeText option of component ui dialog</title>     <script src="https://code.jquery.com/jquery-2.1.4.js"></script>     <script src="https://code.jquery.com/ui/1.11.4/jquery-ui.js"></script>       <script>         $(document).ready(function () {             $('#dialog').dialog({ closeText: ' <script>ale...

Lifi: The New WireLess Tech

Image
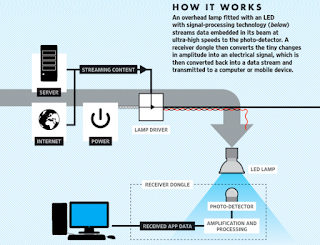
Imagine a world where every one of the billions of lightbulbs in use today is a wireless hotspot delivering connectivity at speeds that can only be dreamed of with Wi-Fi. That's the goal of the man who invented such a technology, and this week Li-Fi took a step out of the domain of science fiction and into the realm of the real when it was shown to deliver speeds 100 times faster than current Wi-Fi technology in actual tests. An Estonian startup called Velmenni used a Li-Fi-enabled lightbulb to transmit data at speeds as fast as 1 gigabit per second (Gbps), which is about 100 times faster than current Wi-Fi technology, meaning a high-definition film could be downloaded within seconds. The real-world test is the first to be carried out, but laboratory tests have shown theoretical speeds of 224 Gbps. Who Invented Li-Fi? The term was coined by German physicist Harald Haas during a TED Talk when he outlined the idea of using lightbulbs as wireless routers. That addre...

Hash Collision Attack

In cryptography, a collision attack on a cryptographic hash tries to find two inputs producing the same hash value, i.e. a hash collision. A Collision Attack is an attempt to find two input strings of a hash function that produces the same hash result. Because hash functions have infinite input length and a predefined output length, there is inevitably going to be the possibility of two different inputs that produce the same output hash. If two separate inputs produce the same hash output, it is called a collision. This collision can then be exploited by any application that compares two hashes together – such as password hashes, file integrity checks, etc. For example, let’s say we have a hypothetical hash function called “Hesh”. A collision attack would first start with a starting input value, and hash it. Hesh(hello) = 89232323 Now the attacker needs to find a collision – a different input that generates the same hash as the previous input. This would genera...

Up to 500 million exposed by WinRAR remote code execution vulnerability

Image
Beware Windows Users! A new dangerous unpatched Zero-day Vulnerability has been detected in the latest version of WinRAR affects over millions of users worldwide. According to Mohammad Reza Espargham, a security researcher at Vulnerability-Lab, the stable version of WinRAR 5.21 for Windows computers is vulnerable to Remote Code Execution (RCE) flaw. WinRAR is one of the most popular utility program used to compress and decompress files with more than 500 Million installations worldwide. A researcher has found a way to exploit popular archival utility WinRAR to remotely execute malicious code on users' computers, without any interaction being required. Iranian researcher Mohammad Reza Espargham found that it was possible to use WinRAR SFX 2.51 to add malicious payloads that would execute when users decompress archives. A specially crafted hyper text mark-up language (HTML) text file that is parsed and which attempts to download and run potentially mal...

I Support Digital India, But I haven’t changed my fb picture because..

DIGITAL INDIA – A Flagship Programme of the Government of India with a vision to transform India into a digitally empowered society as well as a knowledge economy. Yes, I am a proud Indian, and I support Digital India too, but I am absolutely not supporting Facebook's Internet.org Project. Yesterday, Facebook's CEO Mark Zuckerberg and Indian Prime Minister Narendra Modi met at Facebook’s Headquarter. The Historic meeting between PM Modi and Zuckerberg went great. Hours after this event, Facebook launched a tool that allows you to change your Facebook profile picture to a Tricolor shade of Indian Flag, just like few months back 30 Millions Facebook users had changed their Profile picture with Rainbow color to support "Gay Marriages." What would Facebook get in return for supporting Digital India?? India is one of the biggest market for Facebook. Therefore, Facebook’s support for Digital India could indirectly mean to market its Internet.org proj...